
Web Security
28 sites
https://fyr.io/
Matt is a UK sysadmin who runs this ever-evolving personal site covering infosec, the indieweb movement, and life both on and offline. The site features multiple custom themes, a changelog documenting its evolution, technical guides, and a curated collection of favourite corners of the internet to explore.
https://singe.za.net/blog/archives/1016-Killing-the-Evercookie-Part2-MobileSafari.html
Dominic White's technical blog dives into browser privacy and tracking vulnerabilities, with this post investigating how the Evercookie persistent tracking mechanism operates on iOS MobileSafari and embedded WebKit apps. The research reveals significant privacy gaps in Apple's mobile platform and offers practical steps for jailbroken iPhone users to defend against supercookies.
https://technicalinfo.net/tools/index.html
TechnicalInfo.net by Gunter Ollmann offers a comprehensive toolkit for passive information gathering, including domain WHOIS lookups, DNS records, IP address lookups, traceroutes, and bandwidth speed tests. The collection is aimed at security researchers and network administrators, with tools organized around reconnaissance techniques and network analysis.
https://securityxploded.com/art-of-arp-spoofing.php
SecurityXploded is an information security research organization offering in-depth technical articles on topics like ARP spoofing, flooding, and poisoning alongside over 200 free security and password recovery tools. This particular article dives into network-layer attack techniques including MITM attacks and ARP cache manipulation, making it a valuable reference for security professionals and enthusiasts alike.
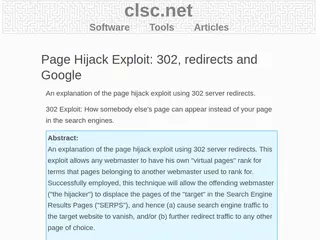
https://clsc.net/articles/google-302-page-hijack.php
Written by Claus Schmidt in 2005, this technical article exposes the '302 page hijack' exploit, a method by which malicious webmasters could use server redirects to displace competitors' pages from search engine results. It covers how the attack works, which search engines were vulnerable, and practical precautions both victims and potential hijackers can take.
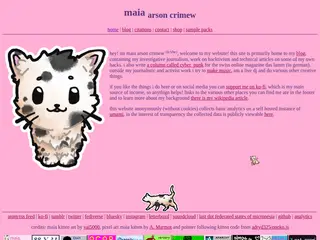
https://maia.crimew.gay/
Maia Arson Crimew is a Swiss hacktivist, investigative journalist, and musician whose personal site serves as a hub for her technical security research, hacking write-ups, and journalistic work including a column for the Swiss magazine Das Lamm. The site links to a blog covering high-profile hacks and hacktivism, music projects, DJ work, and sample packs, making it a fascinating window into one of the more notable figures in modern hacktivist circles.
https://bad.download/
The personal site of bad.download, a tech-industry professional who writes about cybersecurity, privacy, digital preservation, and generative AI models. Minimal but thoughtful in scope, it features links to personal projects like a Discord bot using GPT-4 Vision alongside old-school web nostalgia banners for Firefox, AIM, and WinRAR.
https://shampoo.antville.org/
The personal weblog of Martin Johns (aka Maddin), a security researcher whose posts focus on web security topics including CSRF protection, XSS detection, DNS rebinding, Firefox extensions, and OWASP conference coverage. It offers a window into early-to-late 2000s browser security research, with references to tools like NoScript, LocalRodeo, noXSS, and XSSDS that Johns developed or contributed to.
https://shellsharks.com/
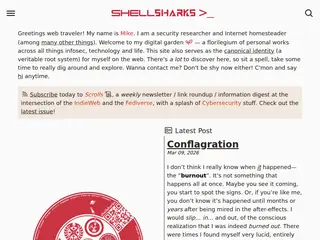
Mike's digital garden at Shellsharks covers infosec research, technology, and personal life across a richly interconnected set of blogs, notebooks, and logs. A self-described 'Internet homesteader,' Mike has built an expansive personal web presence complete with a podcast, linklog, devlog, and Fediverse integration that makes it a compelling destination for security-minded web explorers.
https://websec.ca/kb/sql_injection
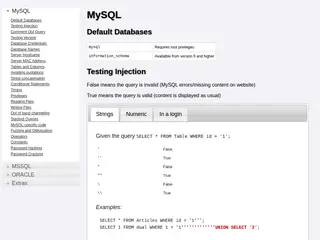
A comprehensive reference covering SQL injection techniques across MySQL, MSSQL, Oracle, and other database platforms, with detailed cheat sheets for testing, exploitation, obfuscation, and prevention. The Knowledge Base is organized as a dense technical reference for security researchers and penetration testers, covering everything from basic injection testing to advanced topics like out-of-band channeling and password cracking.